2025 Password Guidelines
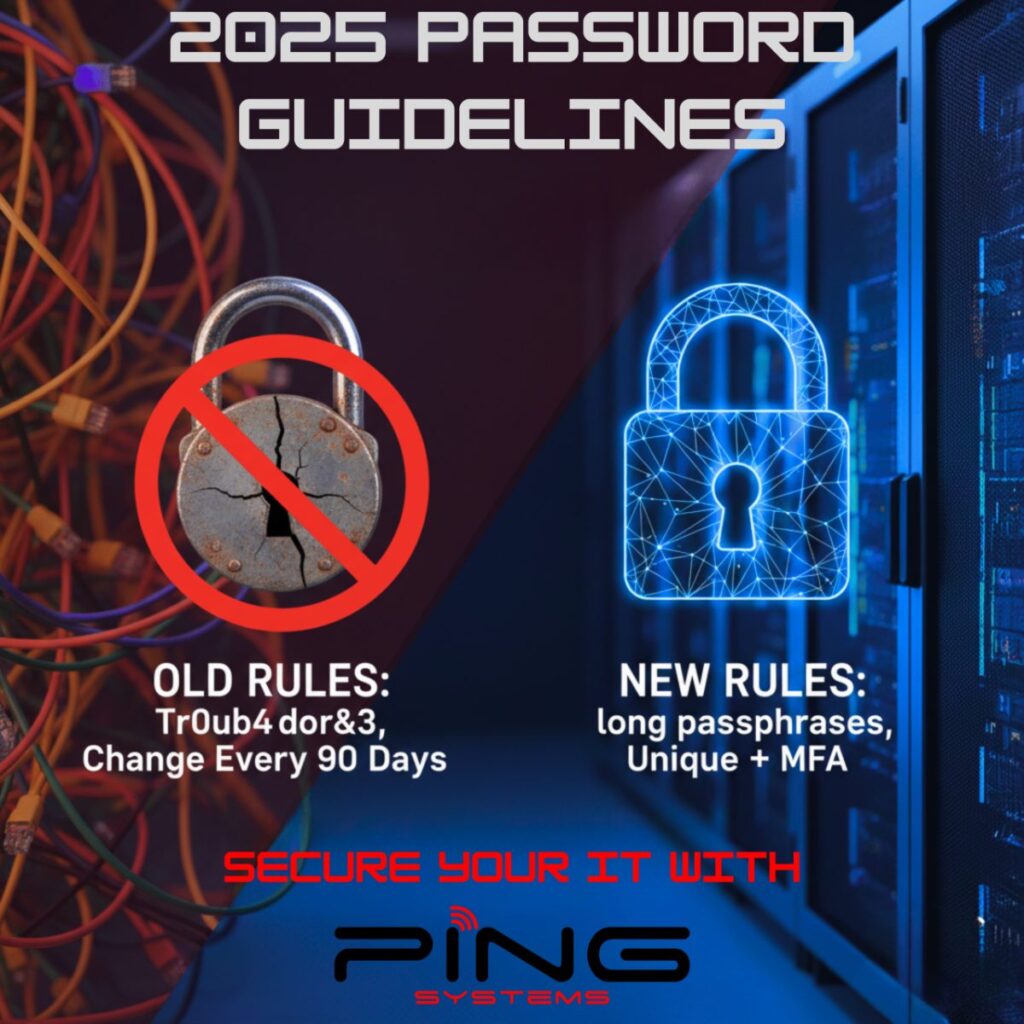
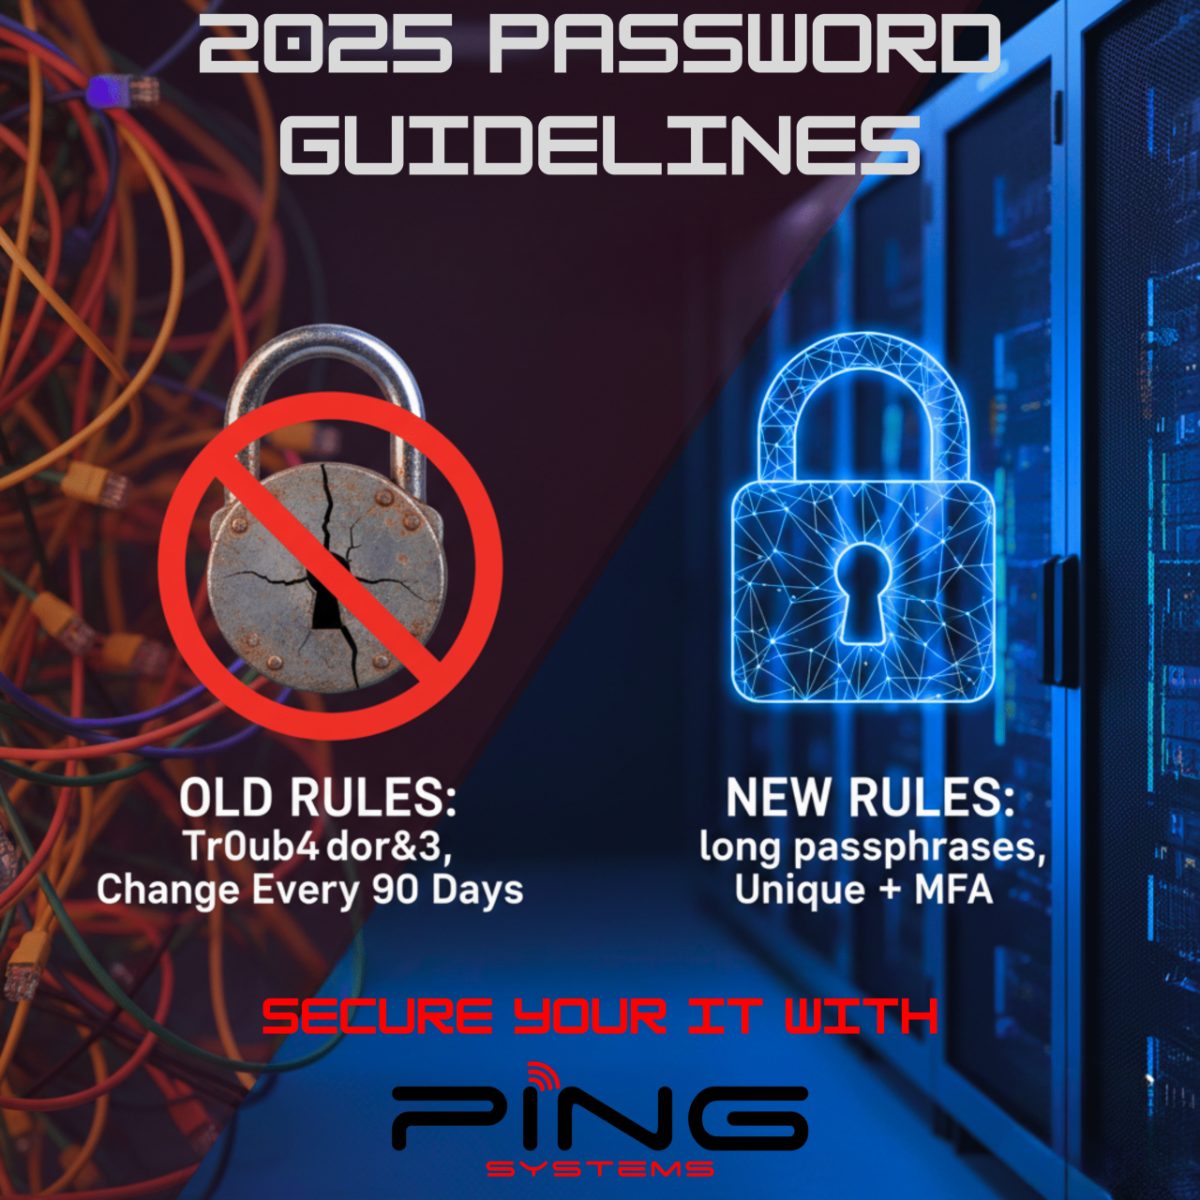
Still making your team change their passwords every 90 days? You might be doing more harm than good.
What changed
Cybersecurity moves fast, and our understanding of what makes a strong password has evolved significantly. NIST has released updated password guidelines for 2025. It is time to ditch the old rules and embrace what actually works.
Your modern password playbook
- Use long passphrases instead of passwords. Think of a memorable four-word sentence. It is far more secure than a short jumble of symbols. For example, “montreal bagels are the best” beats “Fall2025!”.
- Do not change passwords on a schedule. This is a huge shift, but a crucial one. According to the latest NIST guidelines, a longer passphrase that is never changed is more secure than a password that is changed predictably. Only change it if you suspect a breach.
- Use a password manager and turn on MFA. This duo is the gold standard for personal and business security. A password manager handles creating unique passwords, and multi-factor authentication protects you even if a password is stolen.
Make good habits
Your security is only as strong as your habits. Let’s make them good ones.
Source: Proton, NIST password guidelines.
Related services
Want help rolling out better password habits?
Tell us what you have and we will tell you plainly how we would approach it.
Book a time[email protected]2025 CyberSecurity guidelines IT nist Ottawa password Ping Systems
Recent Comments